New GoinVault module · Privacy

Delete what you may. Keep what you must.

Privacy requests under the GDPR and 20 US state laws, with deadlines, a decision for every data category, reply letters and an audit trail nobody can edit afterwards. Built for German firms with US clients.

GDPR20 US state lawsOn-prem agentTamper-evident audit trail
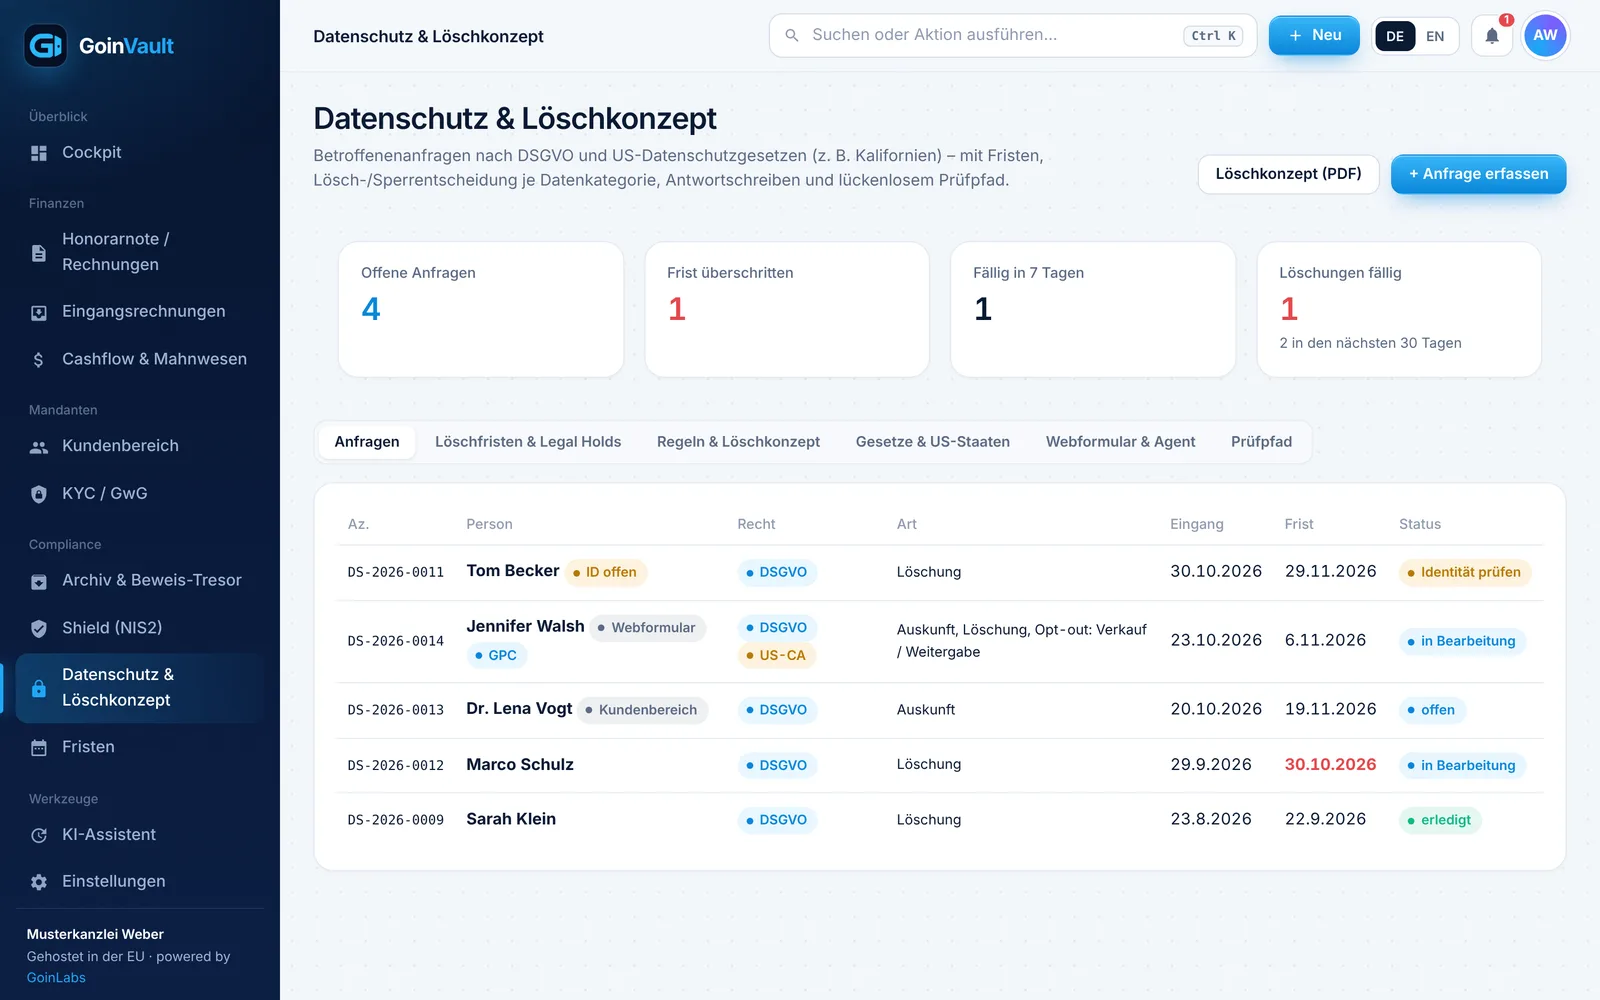
GoinVault privacy requests list with deadlines and laws
The problem

A deletion request is not a delete button.

German law says you must keep invoices, mandate files and anti-money-laundering records for years. The GDPR and US privacy laws say you must delete. GoinVault decides, per data category, what goes and what stays.

21laws in one place: the GDPR plus 20 US state laws in force
10business days for the California receipt deadline, tracked for you
256bit SHA-256 hash chain makes the audit trail tamper-evident
0files leave your office when the on-prem agent searches
Requests

Every request in one queue, with the clock running.

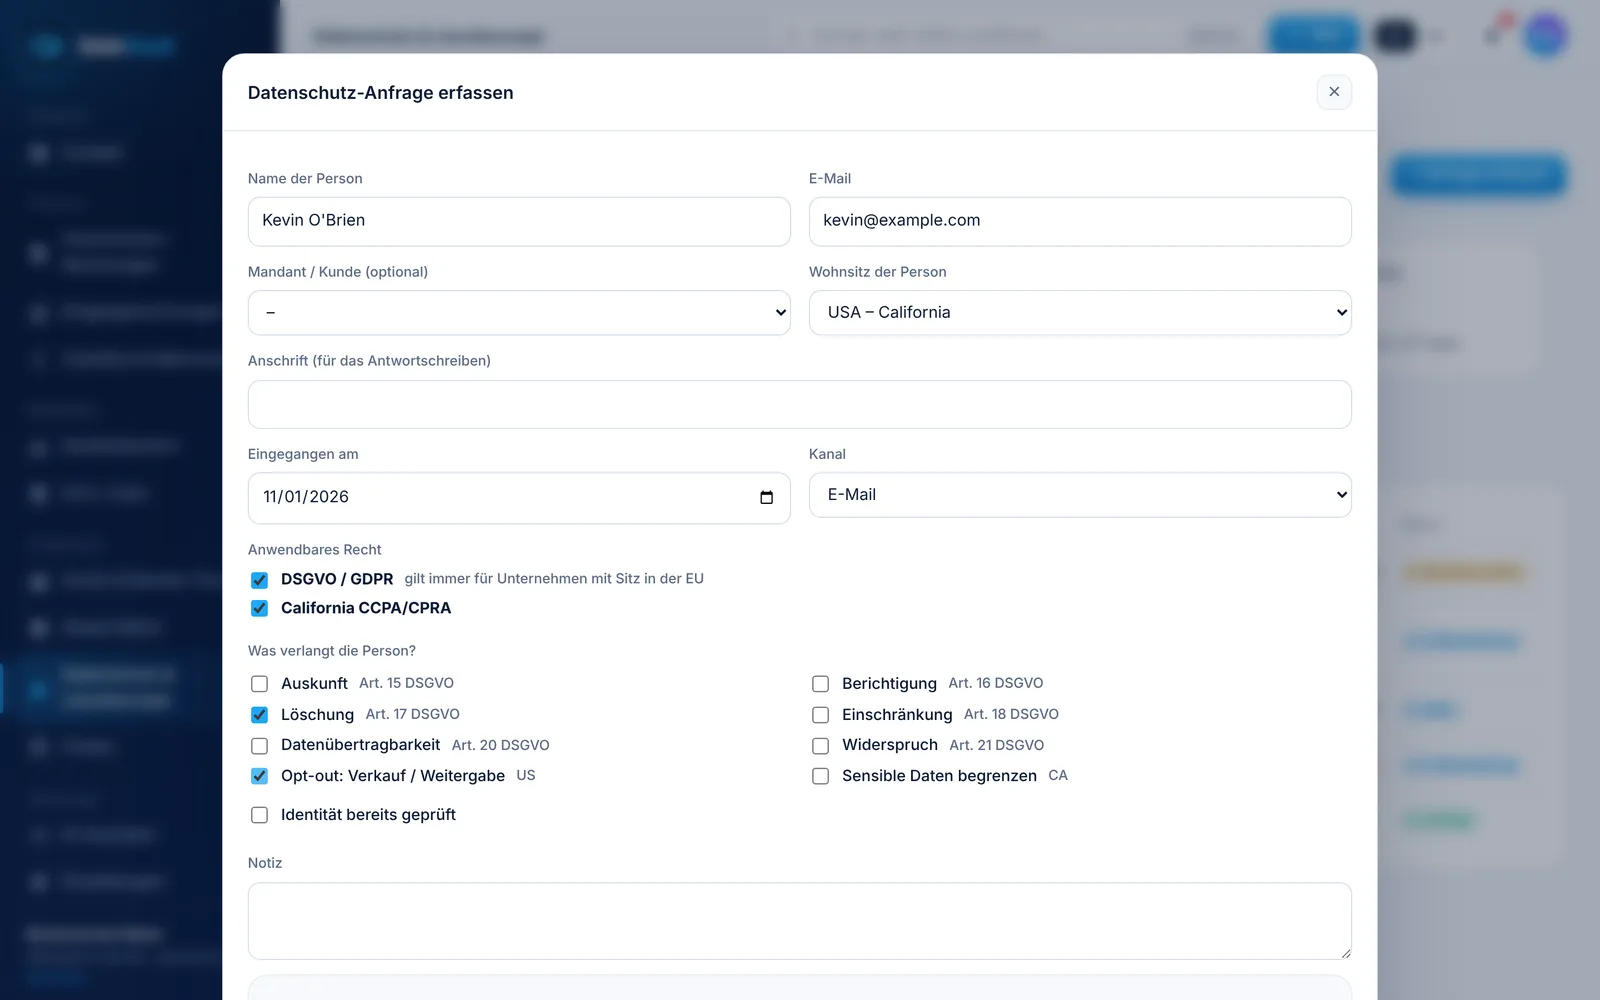
Requests arrive from staff, the client portal or your own web form with an e-mail confirmation link. GoinVault picks the laws that apply and the shortest deadline wins automatically.

Request queue

See what is due before it is late.

Each request shows the person, the law, the type and the deadline. Overdue and due-this-week requests are highlighted.

  • Access, deletion and opt-out of sale or sharing
  • California 10-business-day receipt and 15-business-day opt-out deadlines included
  • Identity check by e-mail confirmation link
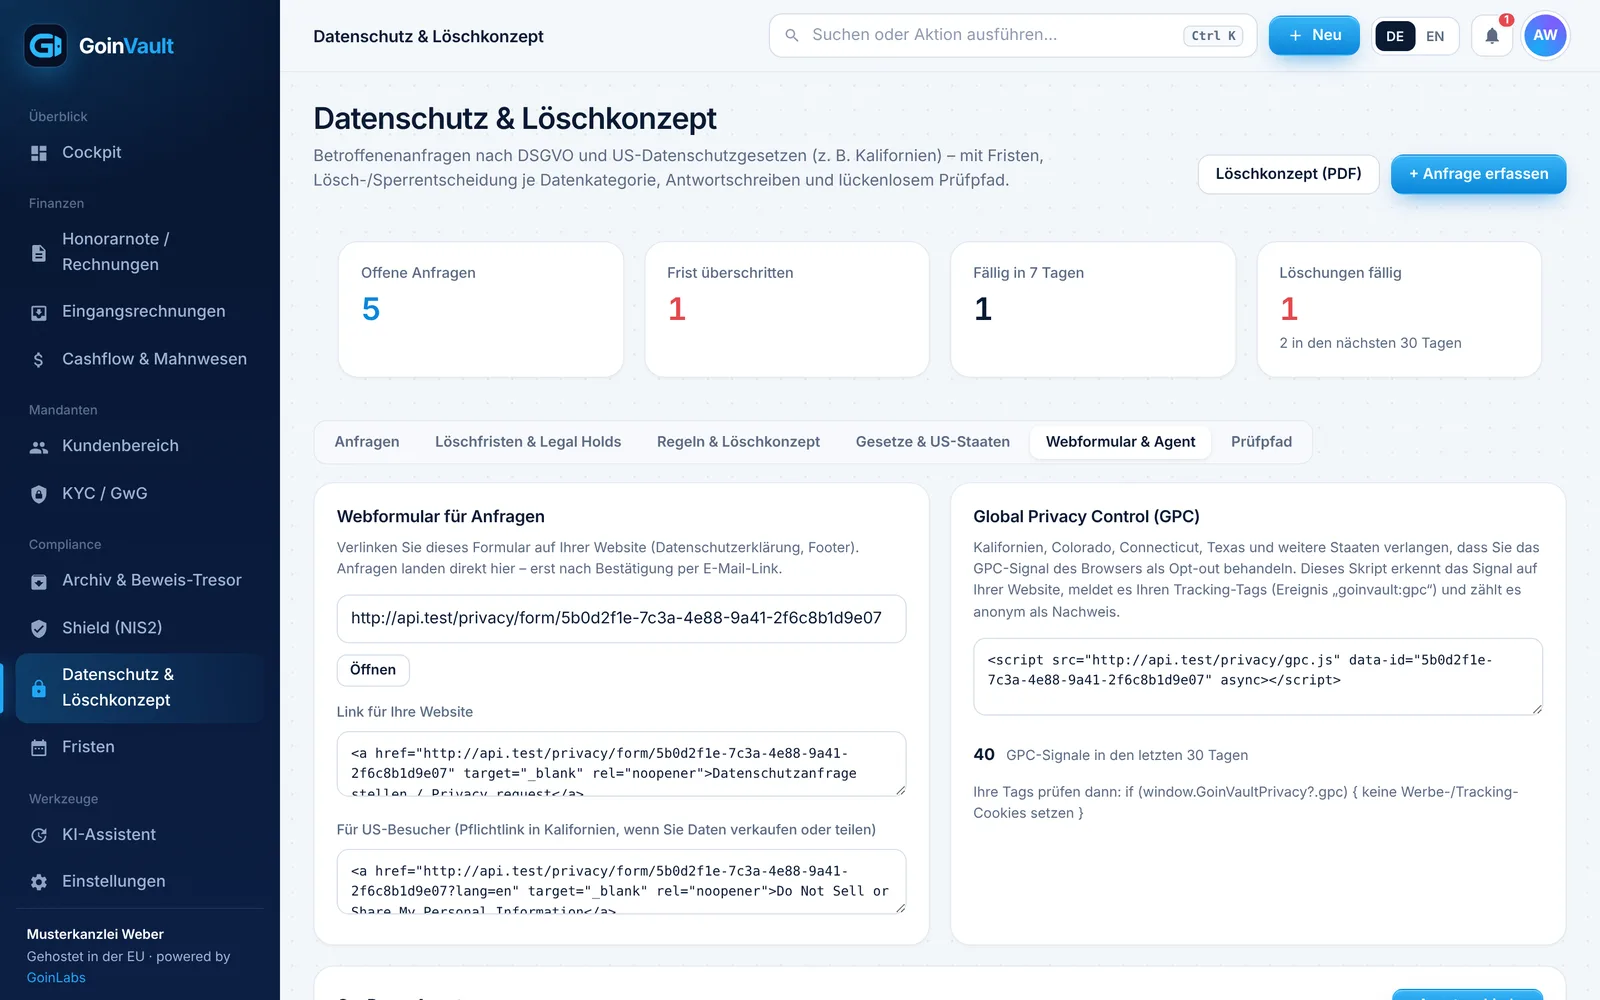
  • Global Privacy Control signals counted as anonymous evidence
New request form
Privacy request queue
Delete or restrict

A decision for every data category.

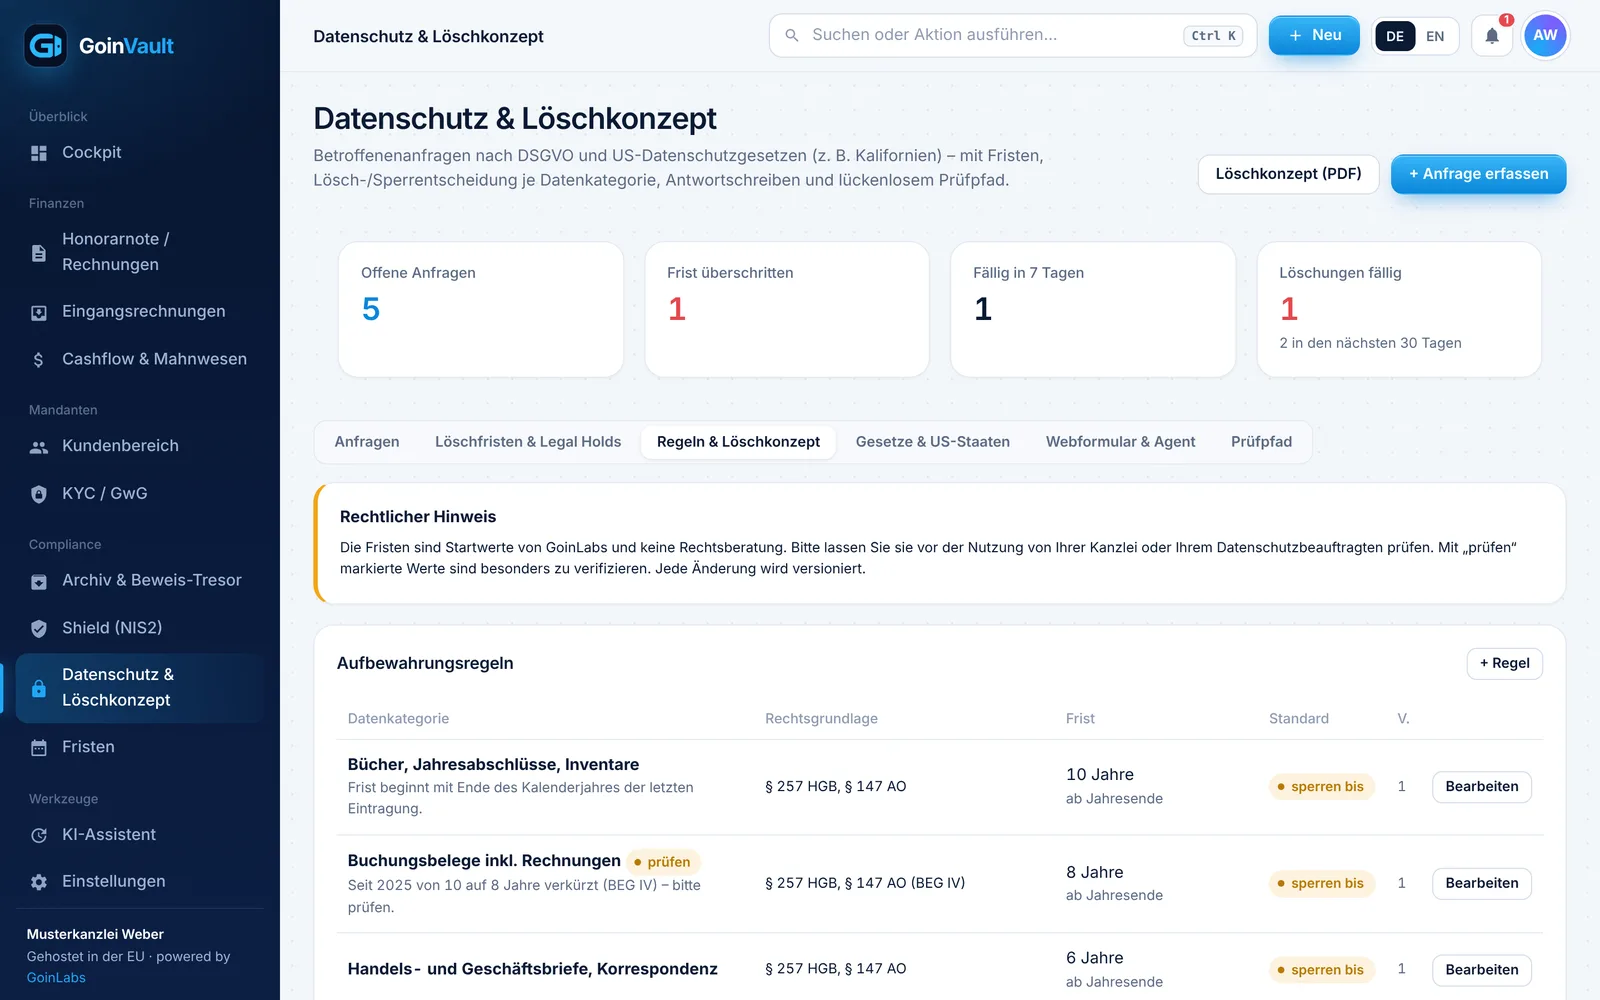
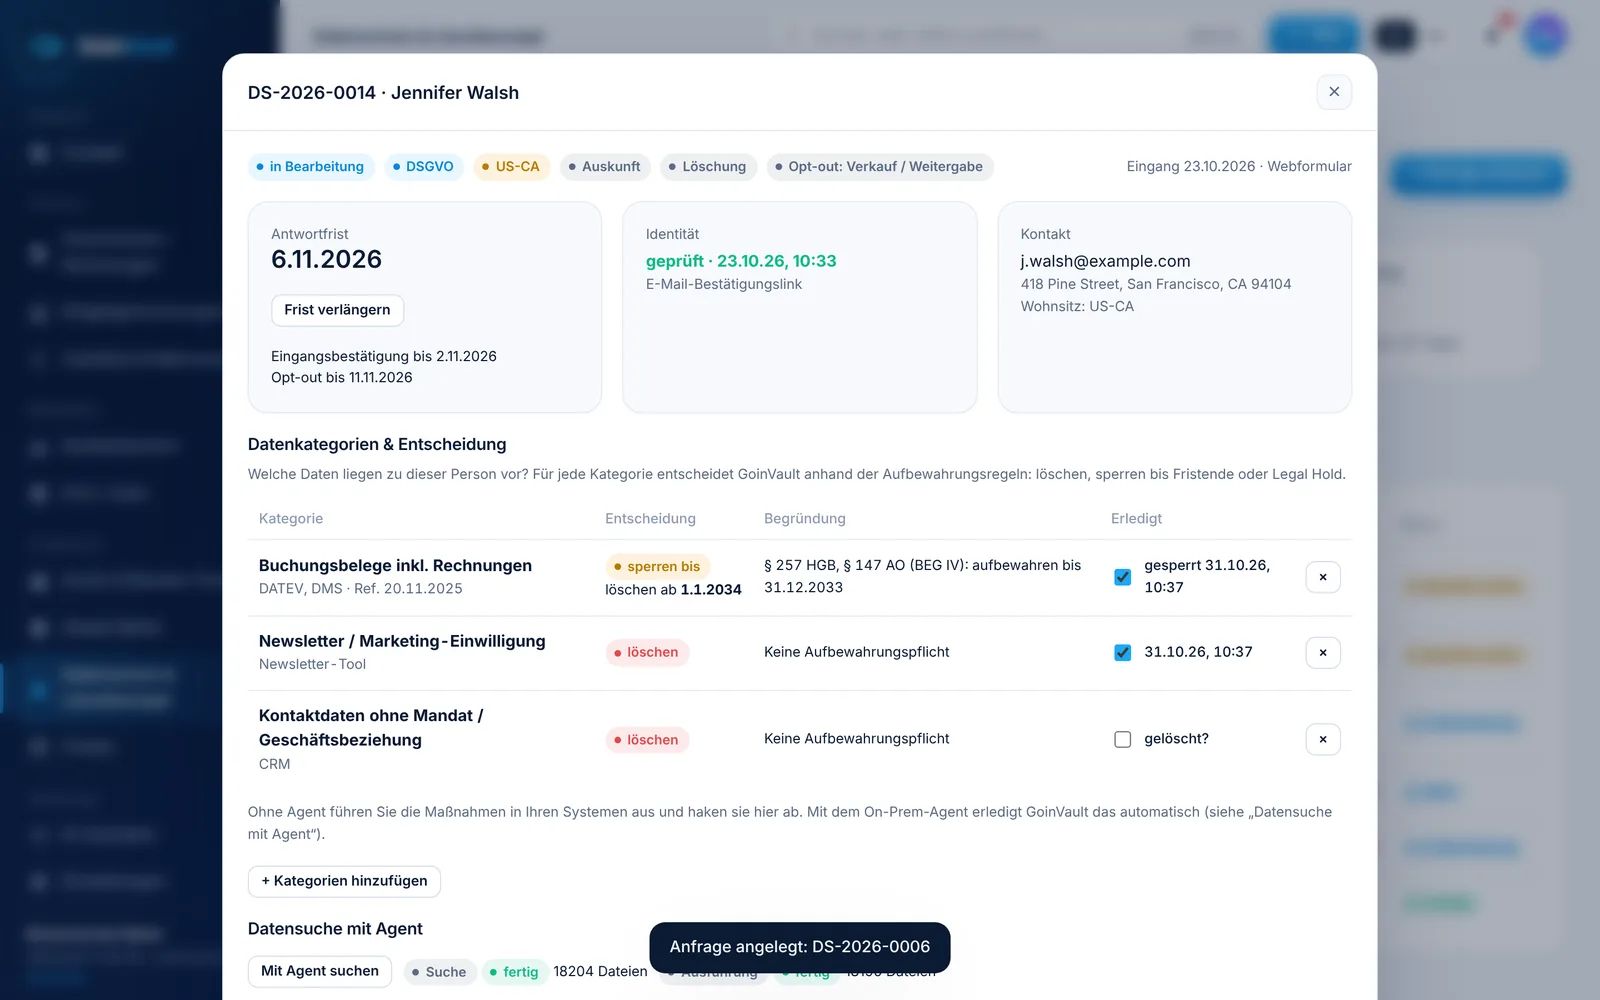
For each category GoinVault applies your retention rules: delete now, restrict until the period ends, or legal hold. Every line shows its legal reason.

  • Statutory periods such as HGB, AO, BRAO, StBerG and GwG built in
  • Rules are editable and versioned
  • Restricted data is locked, with a date for final deletion
Retention rules
Decision per data category with the legal reason
On-prem agent

Find the person in your own systems.

A small Windows agent runs inside your office. It searches folders, e-mail archives, databases and scanned documents for a person, then carries out the deletions and restrictions you approve.

Search

Folders, mail, databases, scans.

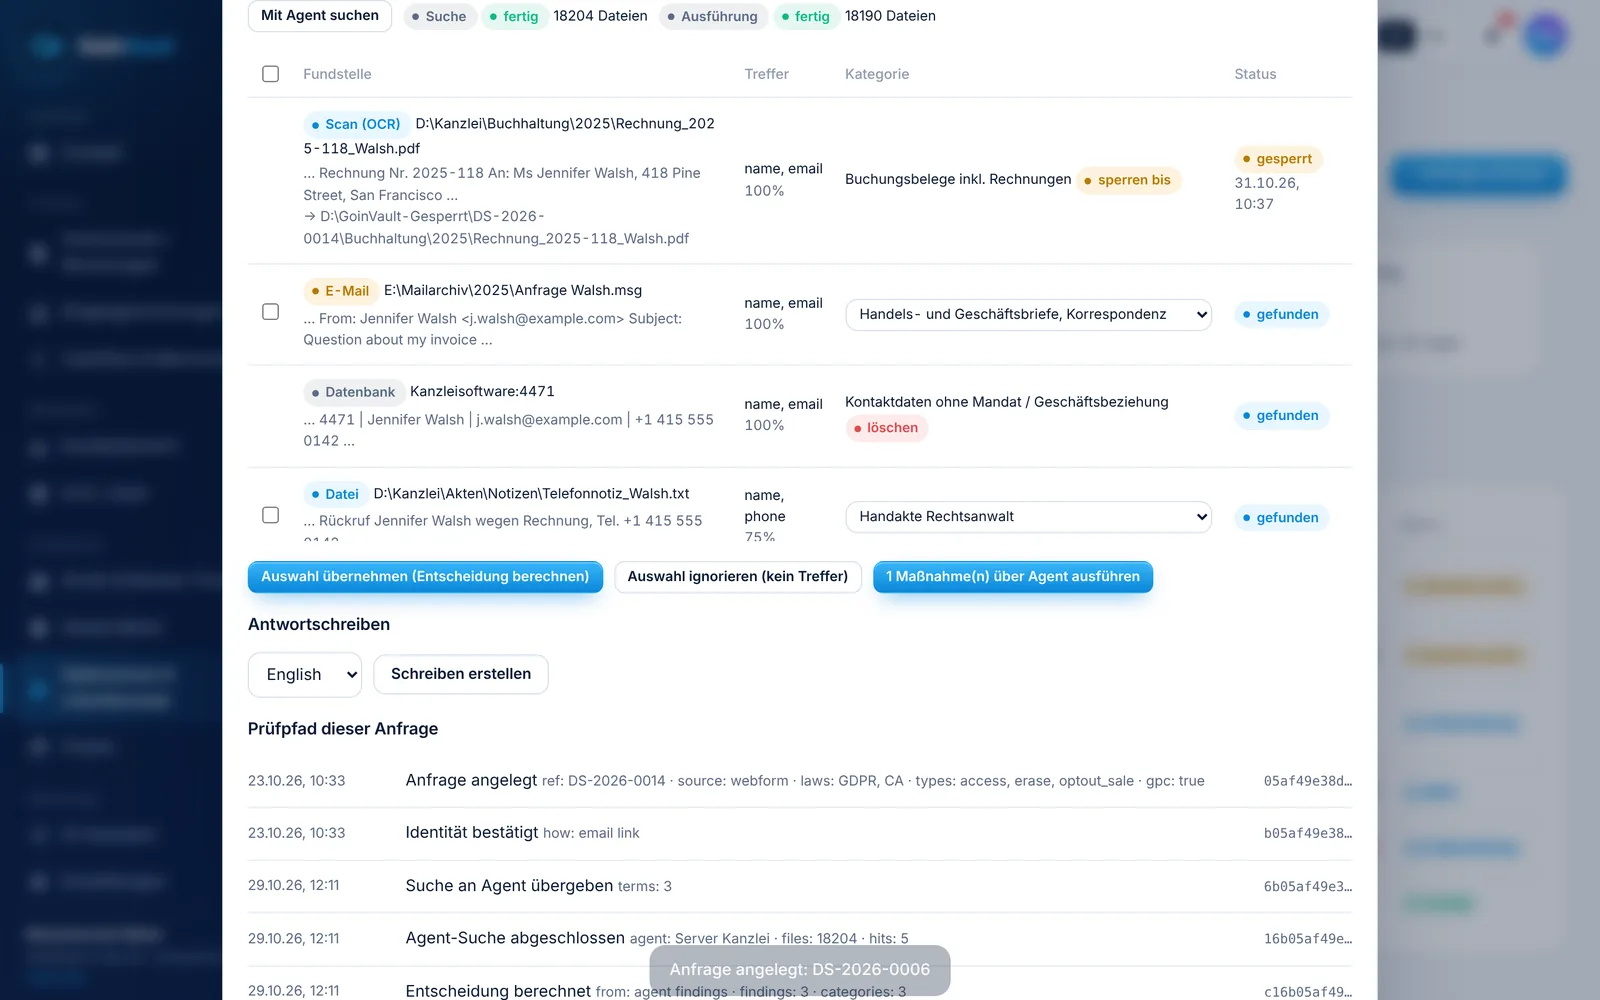
The agent reads .eml, .msg and .mbox archives, SQL databases and scanned documents with OCR. You choose which hits count and which category they belong to.

  • Your files never leave the office
  • Optional local AI such as Ollama
  • A data inventory scan finds files that are past their retention period
Web form and agent settings
Agent findings with category and decision
Reply and prove

Letters, policy and proof.

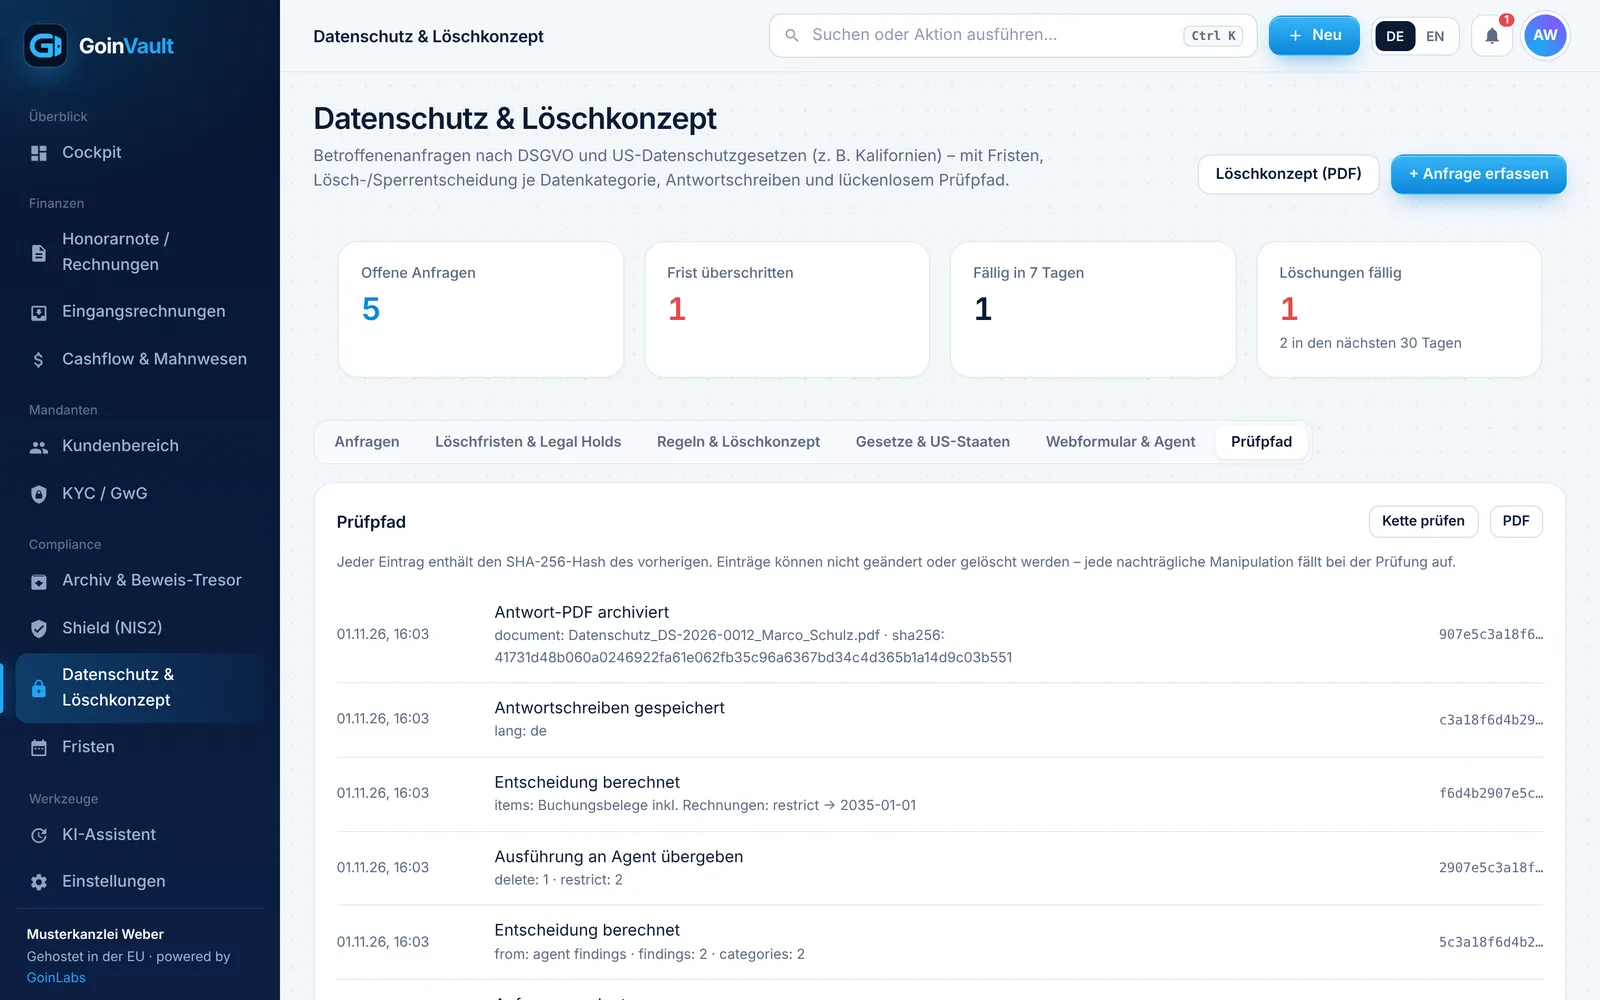
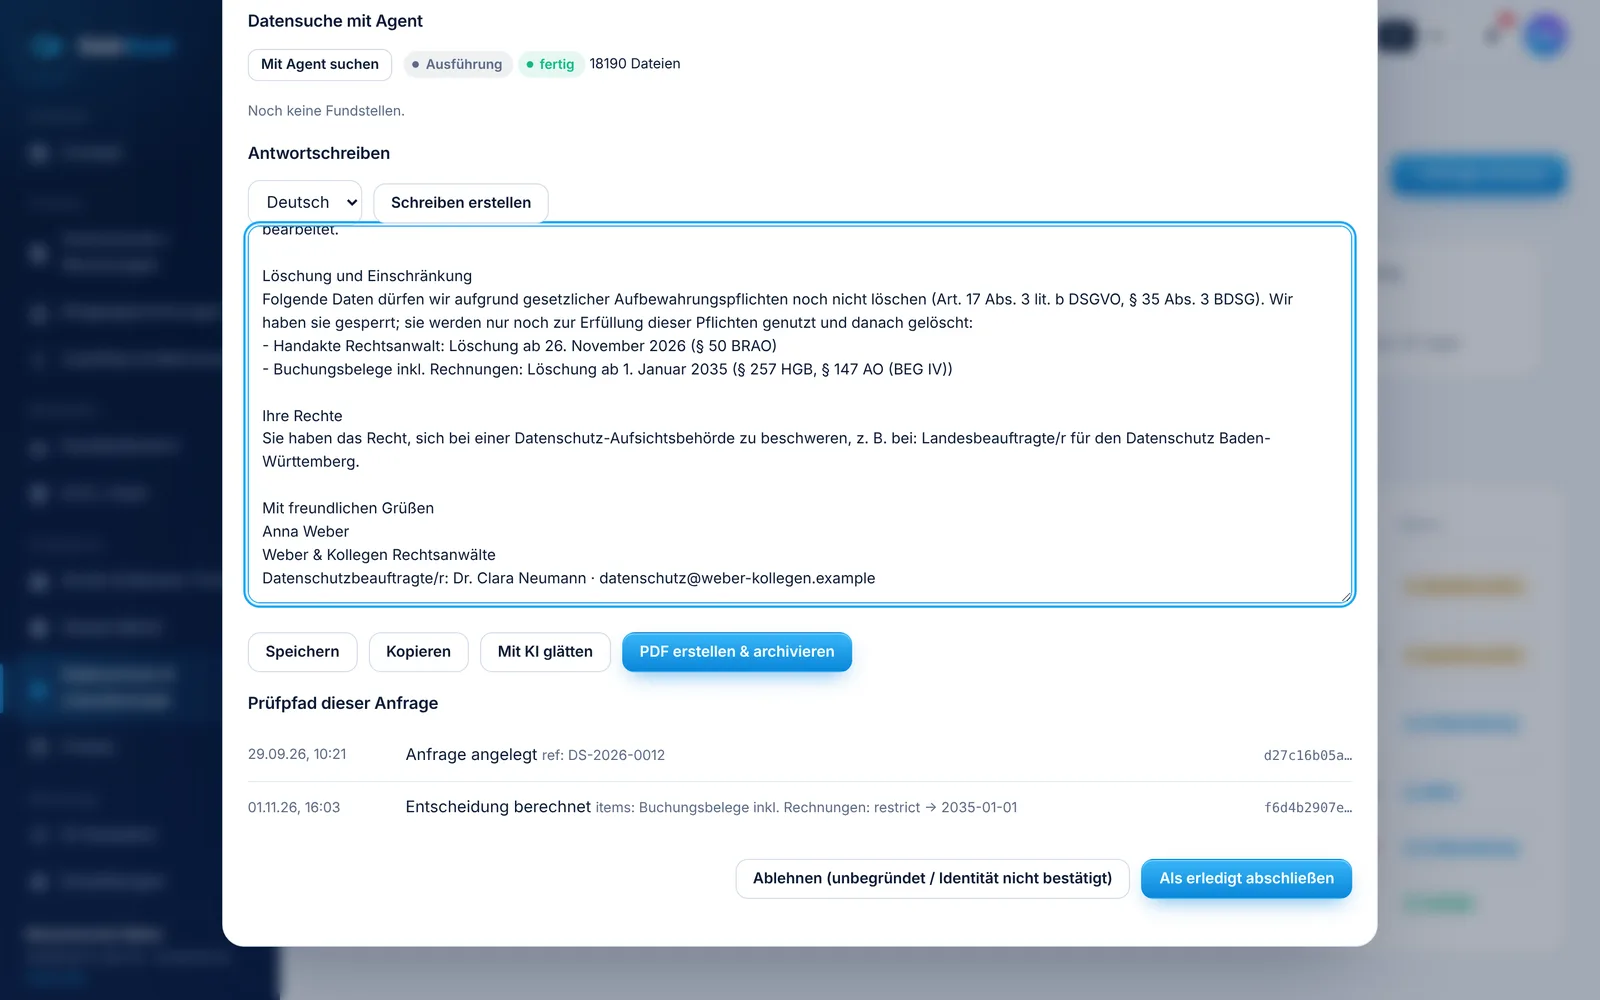
Reply letters in German and English are archived as sealed PDF. A living retention policy PDF is generated from your rules. Every step lands in an append-only hash chain with a one-click integrity check.

  • Reply letters in DE and EN
  • Retention policy (Löschkonzept) as PDF
  • Audit trail export as PDF
Audit trail with hash chain
Reply letter
Deadlines and clients

In the cockpit, on the phone.

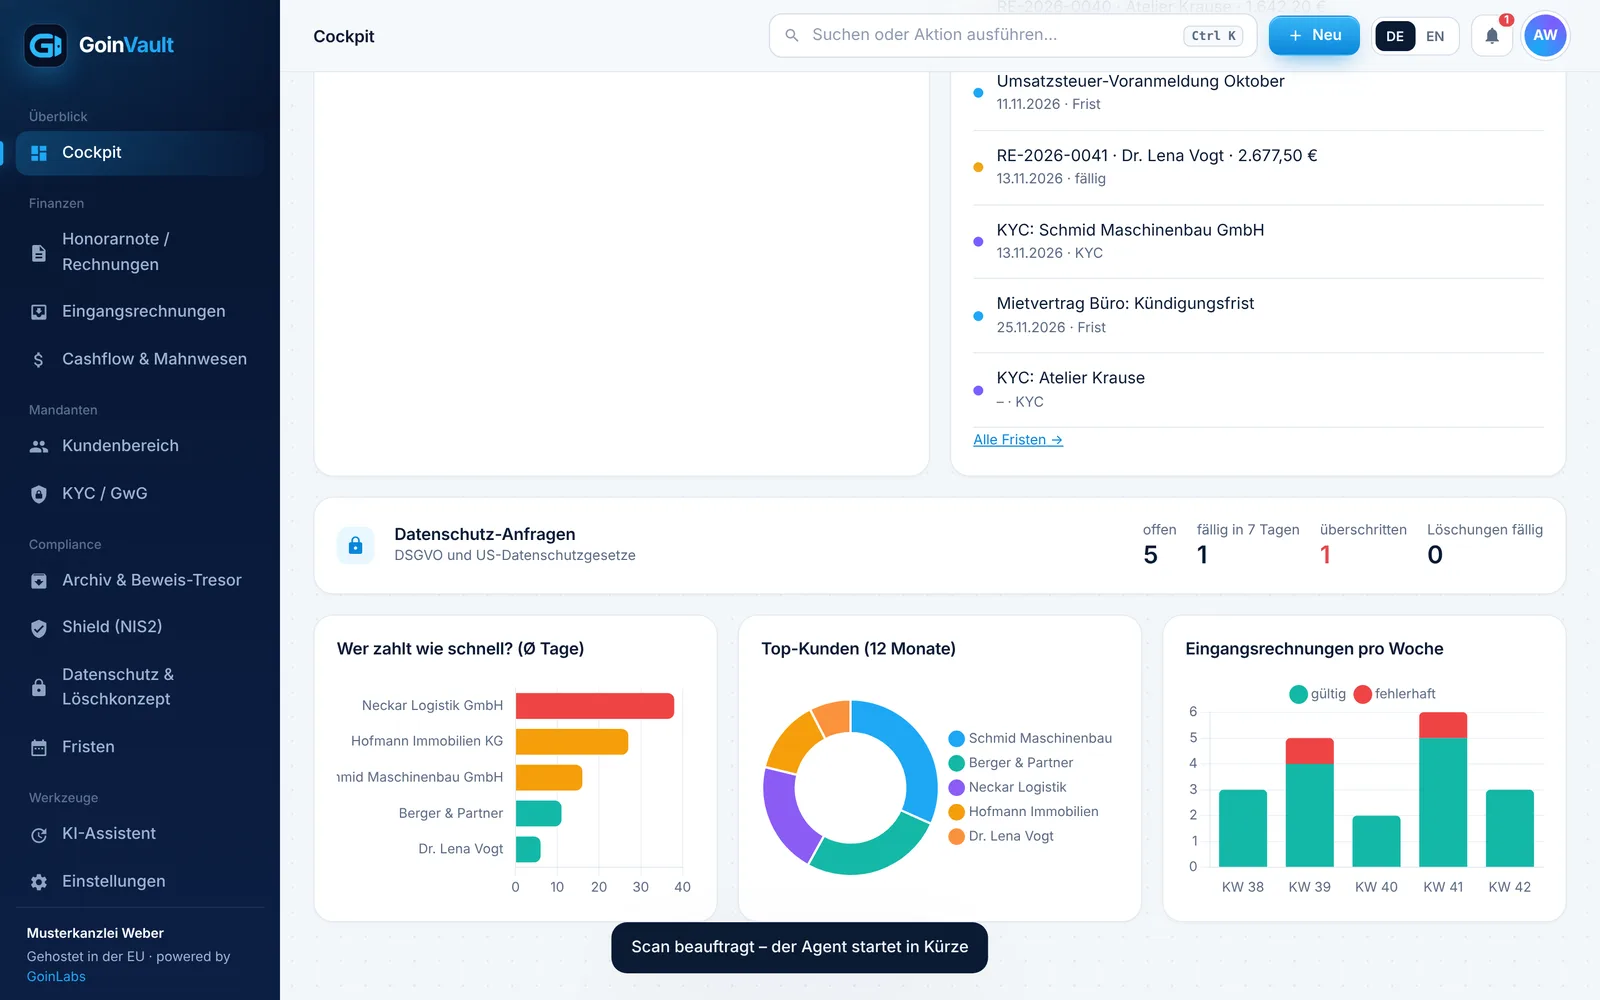
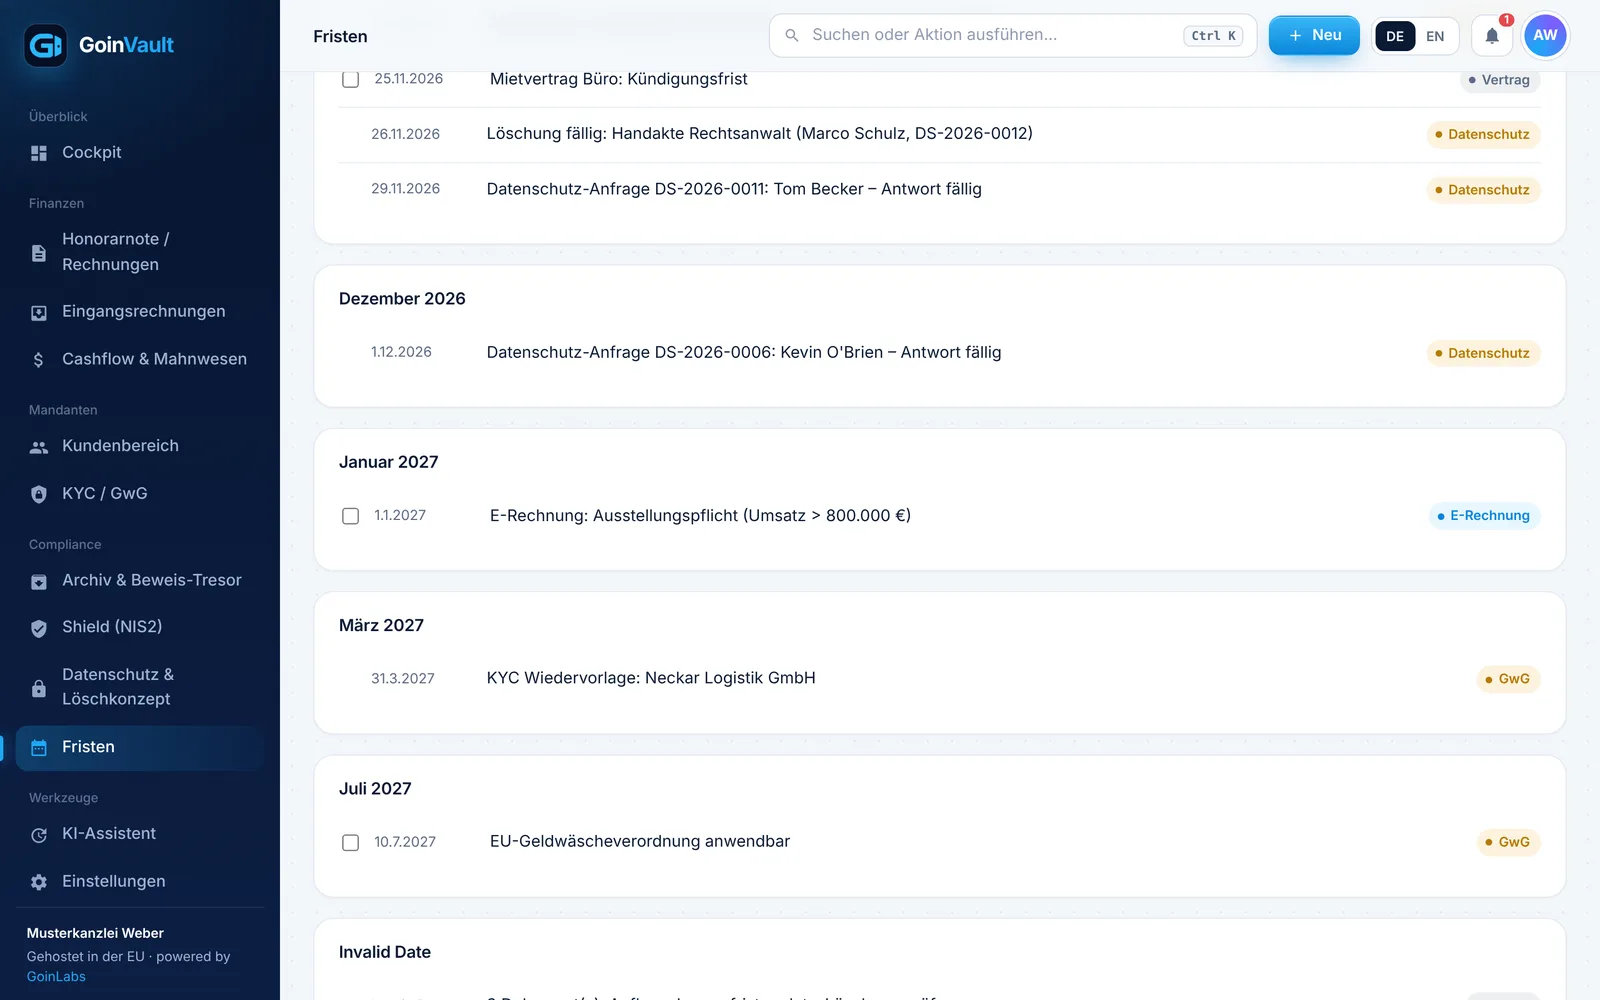
Deadlines show up in the cockpit and the deadline calendar. Your clients can see their own privacy requests in the client area.

  • Retention deadlines and legal holds
  • Client area for requests
  • Works on the phone
Cockpit card
Deadline calendar
GDPRCCPA / CPRAVirginiaColoradoConnecticutTexasOregonHGBAOBRAOStBerGGwGGPC
Two legal worlds

GDPR and US state laws.

German firms with US clients get both layers in one tool. Switch to see what is built in for each side.

Access and deletion

Requests under Articles 15 and 17 with the legal deadline tracked.

German retention law

HGB, AO, BRAO, StBerG and GwG decide what must be kept.

Restrict instead of delete

Data under a duty to keep is locked until the period ends, then deleted.

Data stays in the firm

The agent works inside your office. Documents are not uploaded.

For law firms, tax advisers and consultancies

Prove what you did and why, request by request.

About GoinVault

20 state laws

California CCPA/CPRA, Virginia, Colorado, Connecticut, Texas, Oregon and more, in force today.

Shortest deadline wins

When several laws apply, GoinVault uses the strictest deadline.

Opt-out of sale or sharing

Opt-out requests with their own deadline, plus Global Privacy Control evidence.

Letters in English

Reply letters for US requesters, archived as sealed PDF.

For German firms with US clients

One queue for both worlds, no second tool.

About GoinVault
Get it

Part of GoinVault. Try it with the agent.

The module is part of GoinVault. Download the Windows agent and test it with your own folders.

Requests

Included

Queue, laws, deadlines, web form and client portal intake

Core

Decisions

Included

Retention rules, reply letters, retention policy PDF

Audit trail

Included

SHA-256 hash chain, integrity check, PDF export

Windows agent

Download ~99 MB

Searches folders, mail, databases and scans, then runs approved deletions

Pricing follows your GoinVault licence. Ask us for a quote.

Download the agent

The build story

From a parked idea to a GoinVault module.

  1. 1

    A parked US idea

    It started as a product idea for US privacy requests, then parked.

  2. 2

    The core is rebuilt

    Rules table, request queue, on-prem agent and audit trail became a GoinVault module for German firms.

  3. 3

    US laws as a second layer

    20 state laws were added on top of the GDPR.

  4. 4

    1 Nov 2026

    All four phases finished: requests, decisions, agent and audit trail. Built on a free Cloudflare and Supabase stack, with an Electron agent and local OCR.

Why a module, not a product?

Firms already keep invoices, mandates and client files in GoinVault. Privacy decisions belong next to the records they affect.

Know what you may delete.

Download the agent, or talk to us about GoinVault.